

Tomorrow’s Tech, Today: Innovation That Moves Us Forward
- State-linked actor OVERCAST PANDA deployed the known implant FlowCloud via physical-access tradecraft.
- Initial compromise completed below the running OS, evading endpoint protections like EDR, MFA, and phishing defenses.
- CrowdStrike's Falcon detects FlowCloud only after boot; OverWatch disrupted intrusions but warns activity will persist.
- Mitigations exist: enforce pre-boot authentication, disable external boot in UEFI, enable Secure Boot, use travel-only devices.
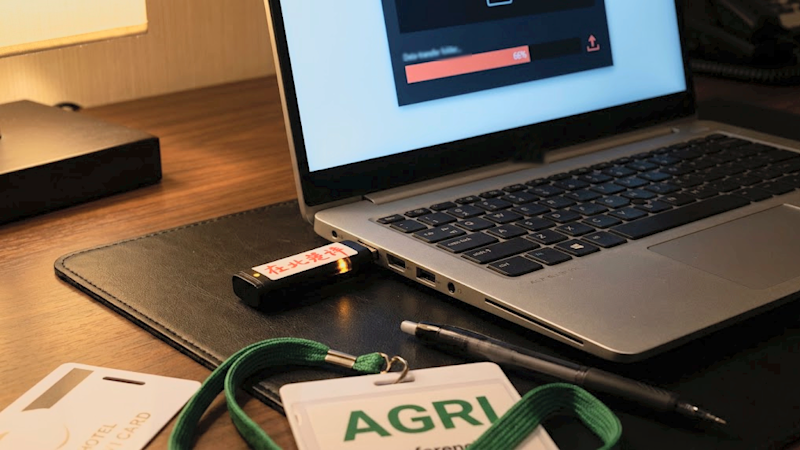
A Chinese state-linked hacking group compromised executive laptops at an agricultural industry conference on Hainan Island this spring — not through phishing or a network breach, but by breaking into hotel rooms and booting the machines from a USB stick while the executives were at dinner.
CrowdStrike, which tracks the group as OVERCAST PANDA, disclosed the campaign in its 2026 Threat Hunting Report and detailed the operation’s timeline in an interview with VentureBeat at Fal.Con 2026: an intruder entered one room at around 8 p.m. local time and a second room by 9:57 p.m., writing a backdoor called FlowCloud directly to each laptop’s storage before rebooting the machines and leaving. There was no network intrusion, no phishing email, and no credential stolen through a login page.
The report dates the intrusions to between March and May 2026, and the timestamps come from Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, who cleared them for publication in the VentureBeat interview. CrowdStrike’s OverWatch team disrupted the intrusions and assessed that OVERCAST PANDA will almost certainly continue. FlowCloud itself predates this campaign by years: Proofpoint documented it in 2020, delivered by phishing to U.S. utilities, and NTT Security’s SOC has tracked USB-delivered infections at overseas branches of Japanese organizations since early 2022.
Security researchers have called physical-access tampering with an unattended laptop an “evil maid attack,” since Joanna Rutkowska demonstrated one with a bootable USB stick in 2009. Physical-access operations are rare across the 290 named adversaries CrowdStrike tracks, according to Meyers, and MUSTANG PANDA‘s version depends on a dropped USB stick the victim plugs in. What Meyers identified as novel is the combination of hotel-room entry by a state intelligence service with malware deployment, booting the target machine from the USB rather than relying on a user to execute a file from it.
When the executives powered on the next morning, the trigger fired and FlowCloud loaded. Keylogging, screen capture, file collection, and credential harvesting began.
“We have the visibility once the machine boots up,” Meyers told VentureBeat. A registry key or similar trigger starts FlowCloud sometime after the operating system loads, and that’s when Falcon’s sensor picks it up. The gap is the window between the USB write and the next boot — the hours the laptop sits compromised and undetected before the executive logs back in.
CrowdStrike published that gap a month before it announced its AI security product slate — Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway — at Fal.Con 2026 this week.
Why existing security tools missed it
EDR needs the operating system loaded and the agent running. MFA waits for a login attempt, phishing training for an email, AI agent security for an agent to secure.
OVERCAST PANDA bypassed all of them at the point of entry. The initial compromise completed below the running OS, below the EDR agent, below the authentication stack. Falcon caught FlowCloud once its process started after boot, but by then the implant and its trigger were already on disk.
“Hotel entry is a very common thing,” Meyers said. “Talk to any corporate physical security person. They’re generally aware of hotel entry, but I think what is unique is the combination of hotel entry with deployment of malware.”
Meyers said he thinks China’s Ministry of State Security sits behind OVERCAST PANDA. The people entering the rooms are either officers or agents of the MSS or the Ministry of Public Security, or hotel housekeeping staff the services have bribed or compelled, Meyers told VentureBeat. A separate mid-2026 intrusion targeted a U.S.-based media professional using the same tradecraft, according to the report. Targeting an agricultural conference aligns with collection priorities Meyers tied to China’s five-year plans.
What CrowdStrike announced at Fal.Con and where runtime security begins
Nvidia CEO Jensen Huang joined George Kurtz on the Fal.Con stage to unveil SafeMind, an agentic cybersecurity system built on Nvidia Nemotron open models and CrowdStrike’s threat data. Meyers told the Fal.Con audience that 7,400 CVEs were registered in June 2026, a 96% increase over June 2025, and that CrowdStrike submitted 2,400 of them via responsible disclosure, roughly 30% of all CVEs registered that month.
Falcon Guardian, the company’s runtime security layer for AI agents on the endpoint, went live the minute Kurtz put the slide up, CrowdStrike President Mike Sentonas told the Day 2 audience, and AI Gateway, listed as a Guardian capability, ships in September as a hosted service with a hybrid version to follow. AJ Shipley, CrowdStrike’s chief product officer, told VentureBeat that CrowdStrike will embed a SafeMind model into Guardian for malicious-prompt detection within the next couple of weeks.
The threats those products address are real, and the report quantifies them. AI agent-triggered detection leads grew at 2.5 times the rate of human-triggered leads, by OverWatch’s count. Cloud-conscious eCrime activity surged 171% over the reporting period. Vishing intrusions doubled in the first half of 2026 compared to the second half of 2025, with the eCrime group SNARKY SPIDER moving from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications.
Every one of those threats is network-based. All of them assume a running OS, an active user session, or a live cloud workload.
The controls that stop this are firmware and policy
“It’s a solvable problem,” Meyers said. “It’s just an inconvenient solution, which means that a lot of people don’t do it.”
CrowdStrike itself has shipped firmware attack detection and BIOS settings auditing through the Falcon sensor since May 2019, including a Dell SafeBIOS integration that surfaces BIOS verification telemetry in the Falcon console. The ability to audit security-related BIOS settings on the laptops executives carry has sat inside the platform for seven years. Pointing it at travel devices is a decision, not a product gap.
The controls that would have blunted the OVERCAST PANDA campaign are old and cheap, and each does a different job. Disabling external boot in UEFI removes the vector. A BIOS administrator password keeps it disabled. Pre-boot authentication lets a foreign boot environment load and still keeps the encrypted volume unreadable until a human supplies the PIN or key. Firmware monitoring detects tampering after the fact.
“Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service,” Meyers advised. He used temporary laptops and email accounts on overseas trips while at CrowdStrike, wiping the device when he returned. The exposure starts at customs. Officials can seize a device and compel a login, he added.
“They have master keys to that stuff,” was his verdict on hotel safes.
Why scale wins the priority fight
Intrusions tracked by CrowdStrike OverWatch grew about 4% over the reporting period, after a 27% rise the year before, a plateau CrowdStrike attributed to a shift toward more complex, resource-intensive campaigns. The OVERCAST PANDA hotel room operation is the example.
The network threat worries Meyers more. Asked to weigh OVERCAST PANDA’s hotel room campaign against the REVENANT SPIDER case he had shown on the Fal.Con stage, an eCrime group using AI to compromise 17 victims with custom web shells in 48 minutes, he picked REVENANT SPIDER.
“You can’t intrude on hotel rooms at scale,” he said. “You can’t intrude on physical devices at scale. And even then, it’s just one device.” The person in the room is the target, and the intrusion rarely pivots further, he added. “REVENANT SPIDER, they’re moving at that speed and they’re using AI across the board, and that’s a whole other threat, and I think that’s more concerning for the average enterprise.”
Network-speed, AI-powered intrusions scale. Physical-access tradecraft does not. Security budgets follow the threat that hits the most machines. The threat that is hardest to detect on one machine gets what is left.
But the executives who attended an agricultural conference in China this spring were the specific targets of a state intelligence service, one that chose the slow, unscalable method precisely because it works where network-based attacks fail.
The conference itself is the threat model
Executives at conferences are the campaign’s targets, and runtime security starts only once the machine boots. The vendors filling the Las Vegas show floor this week were selling that same runtime protection to attendees whose own laptops carry the identical gap.
Organizational fracture is the real problem. Falcon Guardian ships to one team, and BIOS configuration on travel laptops belongs to another. The Agentic IdP rolls out under identity governance while the decision about whether executives carry production-access machines to international conferences sits with a different group. And the budget line that funds cloud-threat defense has nothing to do with travel-device policies.
Meyers has lived both sides. “I’ve talked to companies where they’re like, we’re having a board meeting in Shanghai, and I’m like, why would you do that?”
What security leaders need to do before the next trip
Audit every executive laptop for USB boot status. If the device can be booted from USB right now, it has the same gap OVERCAST PANDA exploited this spring. The steps below cover Windows laptops, the platform FlowCloud targets.
Enforce full-disk encryption with pre-boot authentication. BitLocker in a TPM-only configuration is a documented weak point against physical access. SCRT researchers pulled the volume master key off the LPC bus with a $49 FPGA module in 2021, and Dolos Group did the same over SPI that year. OVERCAST PANDA wrote a backdoor and its post-boot trigger to the Windows volume, so the operators had write access to it. That points to machines that were either unencrypted or protected by a configuration the operators defeated. Pre-boot authentication with a PIN or USB key forces a human step before storage becomes readable.
Verify Secure Boot is enabled and the revocation list is current. Secure Boot validates signatures on boot components and blocks most unauthorized bootloaders, but it leaves external media bootable and signed shims can still carry a bypass. ESET published findings on 11 legacy Microsoft-signed UEFI shims in July 2026 that let untrusted code run at boot on any machine trusting Microsoft’s third-party certificate. Microsoft revoked them in its June 9, 2026 DBX update, so a laptop that skipped that update still trusts them. Lock the boot order at the UEFI level, disable one-time boot menus, and set a BIOS administrator password that covers both the setup utility and any boot-override key. Meyers’ read is that a lot of these settings go unchecked because the fix is inconvenient.
Issue travel-only devices for international conferences with no access to production systems, no saved credentials for internal tools, and no persistent VPN configuration.
“If they can get their hands on it, they can own it,” Meyers put it, citing an old DEF CON adage. Falcon catches FlowCloud only after boot — the exposure is the hours between the USB write and the next login, while the laptop sits closed and compromised.
“It’s cheap to buy a couple of laptops and a couple of phones,” Meyers said. The controls that close that window are a handful of firmware settings and a spare laptop. The question is whether anyone has deployed them.
Read the full article on the original site
